The NIS2 Directive has the potential to be a cornerstone of the EU’s cybersecurity strategy, driving improved security and resilience across Member States. However, fragmentation in national approaches risks undermining the Directive’s objectives and creating unnecessary burdens for businesses, particularly those operating across borders. For the Directive to succeed, consistency in transposition and alignment on shared standards must be prioritised. By addressing the implementation challenges, the EU can not only strengthen its cybersecurity posture but also create an environment conducive to innovation, investment and growth in the digital age.
Overcoming the fragmentation of the NIS2 transposition

Related items

Position Paper
10 Nov 2026
Making web scraping rules work for AI
The European Data Protection Board’s draft guidelines on web scraping for generative AI are an opportunity to provide greater legal certainty and support Europe’s AI competitiveness. However, some proposed requirements risk creating disproportionate burdens for AI developers.
A pragmatic, risk-based approach is needed to ensure the rules reflect the technical realities of AI development. This includes proportionate transparency obligations, recognition of the need for diverse training datasets and greater alignment with the AI Act and Digital Omnibus. Clear, harmonised rules are essential to protect personal data while enabling innovation.
Read our consultation response to learn more about the recommendations.
News
6 Nov 2026
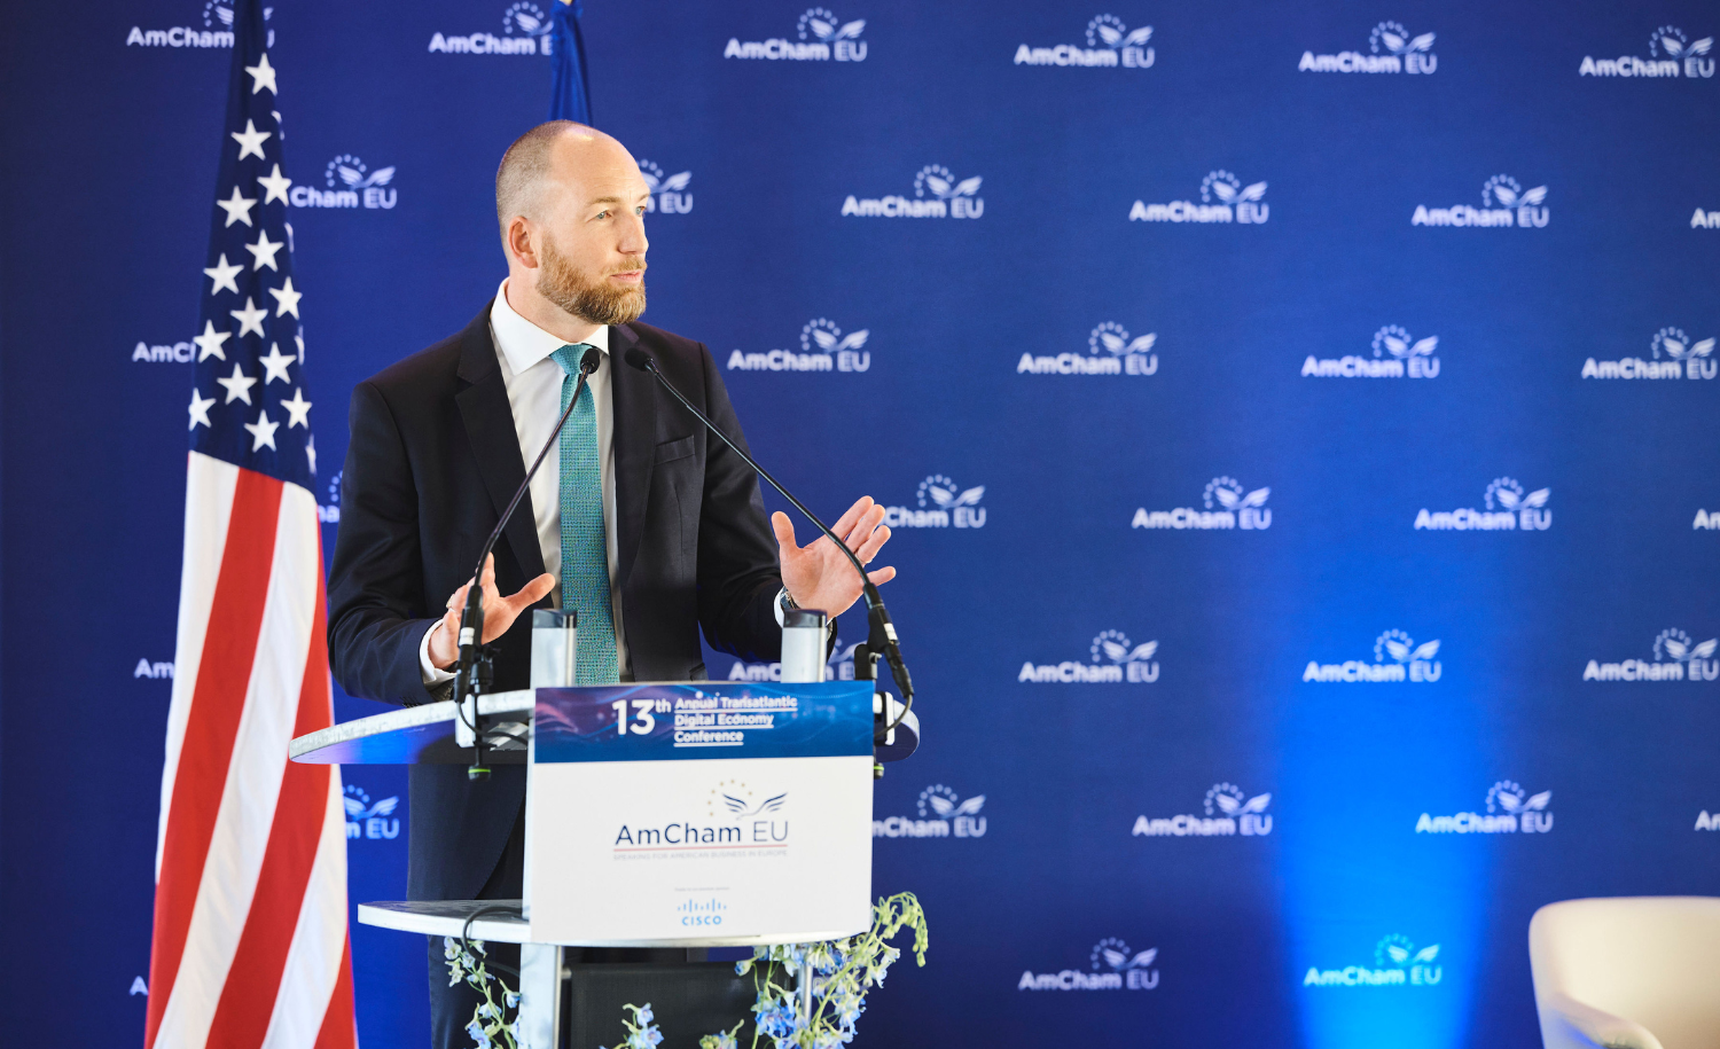
Digital Economy Conference 2026: in review
AmCham EU’s 13th Annual Transatlantic Digital Economy Conference took place on Thursday, 5 November, under the theme Cutting through complexity. The event brought together policymakers, regulators and industry leaders to discuss how clear, workable frameworks and closer EU-US cooperation can bring more coherence to the digital landscape and support economic growth.
Position Paper
7 Oct 2026
Making CADA’s sovereignty framework work for Europe
The success of the Cloud and AI Development Act (CADA) will depend on whether its sovereignty framework strengthens Europe’s resilience and competitiveness without restricting access to the technologies, providers and operating models needed to support the bloc’s digital transformation. As currently envisaged, several elements of CADA introduce origin-based restrictions that are not necessarily linked to genuine sovereignty, security or resilience risks. These measures could reduce competition, increase costs and slow cloud and AI adoption – ultimately working against CADA’s underlying objectives.
A sovereignty framework built on objective, risk-based criteria will better support Europe’s competitiveness, resilience and digital transformation than one based on origin, ownership or nationality.
Policy priorities
Insights and advocacy driving Europe’s policy agenda. Our priorities support growth, innovation and a stronger transatlantic economy.
Membership
Connecting business and policymakers to strengthen the voice of American companies in Europe.